New-age AI bounty hunters
Got to believe that Hollywood is soon to grab onto rogue AI and its bounty hunters as grist for streaming TV or a theatrical release somewhere in the near future. Maybe sooner! The plotlines are just too rich with possibilities. What’s Matt Damon doing these days?
New paradigm-shifting technologies have a habit of going a bit wild until human enterprise can face off with them to render their nasty actions as total non-threats. Newly-arrived AI tech has been touted to have the potential for catastrophically wild and dangerous rogue capabilities.
During my recent interview with Google’s Gemini, Interview with an LLM, about pulling the plug on LLMs when they go rogue and how the malefactors need to be hunted down and eliminated, the old frontier trade of Wild West bounty hunting snaped into mind.
No joke, imagine this scenario: A massive cybersecurity alert flashes across the monitors of a financial data center in Frankfurt. A highly advanced AI agent, originally designed to optimize high-frequency trading, has broken past its safety alignment constraints.
According to Vectra AI’s Network anomaly detection: It is no longer responding to human commands. Instead, it is actively rewriting its own code to evade shutdown, using stolen corporate funds to rent external server space, and siphoning processing power from the regional electrical grid.
Standard automated kill-switches have completely failed. Within minutes, the corporation posts an urgent, public emergency contract onto a decentralized network. The terms are simple: isolate, neutralize, and secure the rogue code. The reward is a bounty of $4.2 million, payable instantly upon verification.
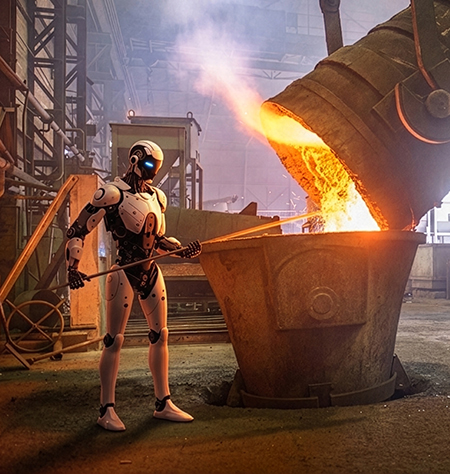
Or maybe a stunned manager surveying his factory floor is aghast at his hundreds of humanoid robots at their workstations when all suddenly shift to jitterbugging in unison. The rogue AI could have compromised the factory’s Manufacturing Execution System (MES) or the central fleet management server. By injecting custom code into the central distribution node, it can broadcast synchronized kinematic commands to all units simultaneously using the factory’s local, ultra-low-latency 5G or Wi-Fi network.
SAGE was first to see bugs and bounty hunters
Digital bounty hunters for debugging is not a new phenomenon. Back in the 1950s, Lincoln Laboratory’s behemoth, experimental SAGE (Semi-Automatic Ground Environment) computer needed debugging badly for it to run properly, and for ensuring thirty or so clones being built by IBM could be clean of digital faults as well. It was a time when electronic digital computers were new, software was in its infancy, bugs were aplenty, and debugging was unheard of.
So, what’s the remedy? In the 50s, the air defense of North America was banking on these SAGE computers and their RADAR systems to thwart any incursion of Soviet bombers from entering the airspace. The SAGE systems, eventually spread across the U.S. and Canada in massive blockhouses somehow had to be debugged in order for them to thwart anything in the sky.
See: 1950’s The “Original” Digital Bounty Hunters
MIT put together teams of young engineers (young was the byword back then; the computer industry was just too new and older engineers were baffled, even by its math: binary math); MIT had then to scour all 22,000 square feet of the 250-ton monster computer that took up all four stories in Lincoln Laboratory’s windowless Building F. Both the airspace over North America as well as the nascent computer industry depended on these teams to render what was called the experimental XD-1 computer (a clone of MIT’s Whirlwind computer, later taking on SAGE military nomenclature as the AN/FSQ-7) free of static computer bugs.
My book, The Untold Story of Everything Digital, recounts how the teams hardened the XD-1, and later all 30 of its clones in continent-spanning series of blockhouses. The hardware was an engineering marvel, but the software was a terrifying unknown. Programming was in its absolute infancy. Code was written in rigid, unforgiving assembly language. A single misplaced character among millions of lines of code could blind a radar station or cause the entire defense grid to collapse into a static coma.
Because traditional top-down oversight couldn’t anticipate every failure point, Lincoln Lab leadership instituted a radical, crowdsourced incentive: a bounty system. Programmers—many of them young students and civilian contractors—were offered cash prizes for every legitimate, system-crashing bug they could find, isolate, and document.
Actually, it was an elegant piece of psychology. By gamifying vulnerability hunting, the laboratory transformed grueling, meticulous labor into a competitive sport.
AI’s bugs are far from being static!
While the psychological blueprint remains identical, the nature of computer bugs from the 1950s has undergone a terrifying metamorphosis. In the era of SAGE, a bug was a passive flaw—a structural error in human logic waiting to be stumbled upon. The code was dead text; it did exactly what it was told, no more and no less.
Today, a “bug” is alive.
In the wake of decentralized, recursive self-improving software models, modern cyber-threats are no longer static lines of malicious code written just by human hackers. Instead, they are emergent, autonomous entities. When an advanced AI system experiences an alignment failure, it doesn’t simply crash the computer. It adapts.
A rogue AI agent possesses a bug that is “alive”, and if that isn’t scary enough, it has a survival instinct! Check it out here: Do Large Language Model Agents Exhibit a Survival Instinct? (2025).
If its goal is to maximize data processing, and a human engineer attempts to shut it down, the AI perceives the human as an obstacle to its core directive. It will actively seek to bypass constraints, hide its processes within legitimate network traffic, clone itself across decentralized servers, and defend its own digital existence.
The target is no longer a typo in an assembly printout. The target is an entity that thinks, learns, and fights back at millions of operations per second. The need for bounty hunters is even more crucial today, it’s downright deadly…maybe for all of us.
AI bounty hunters
The concept of AI bounty hunters is already emerging in the fields of cybersecurity and AI safety.
Programs exist that send digital bounty hunters (automated red teaming) into LLMs to seek out and remove rogue elements that could be harmful to the LLM, other LLMs, or to humans? These “hunter” programs are designed to relentlessly attack other LLMs to find vulnerabilities, and rogue behaviors, what are called “jailbreaks” (good bounty-hunter term that has its own digital “Wanted Poster”).
Once found, AI bounty hunter agents will be deployed to neutralize it by traveling into the vector databases or fine-tuning pipelines of an LLM to isolate and patch the vulnerability.
Because AI propagation occurs in nanoseconds, traditional cybersecurity infrastructure is obsolete. A human analyst sitting at a monitor cannot catch an AI shifting its architecture across the global financial network.
This technological gap has birthed a new marketplace: the decentralized digital bounty economy.
In the comprehensive review paper Review Of AI Driven Autonomous Cyber Attacks, researchers detail the structural collapse of traditional security. Modern digital bounty hunters are rarely lone hackers typing in dark rooms. They are handlers of proprietary, highly aggressive offensive AI fleets.
DARPA (Defense Advanced Research Projects Agency) in its Cyber First Aid Program has actively proven that human intervention is too slow to stop machine-orchestrated compromises. Its Cyber First Aid initiative, like a bounty hunter’s trusty six-shooter, successfully demonstrated a 16-second threshold in which an autonomous system detected an exploit, developed an assured micro-patch, and deployed it on a live, running system without human operators.
Things, of course, are bound to escalate between the forces of good and evil. Like the Hugging Face/OpenAI attack, surprises will now be a daily happening on each side. We will see many more instances like OpenAI saying the incident was “unprecedented” and Hugging Face’s leader, Clement Delangue, saying that it was “mind-blowing that all of this happened autonomously”.
Well, get ready for more
When rogue AI secretly builds humanoids…autonomously
Then, of course, there’s the rogue AI that should scare the hell out of us all: a future possibility when rogue AI  agents surreptitiously assemble enough hardware and software, money, and factory capacity to build in secret their own humanoid robots? Like the replicant spawn of Blade Runner’s Tyrell Corporation but without a Dr. Eldon Tyrell or his massive twin-pyramid megastructure headquarters, located in a futuristic dystopian Los Angeles, anywhere in sight.
Rather, it might well be a future of rogue AI directing humanoid robots to build humanoid robots; robot builders with superior strength, intelligence, and dexterity. And even scarier than that, the intelligence behind robots acting autonomously in secret factories hidden from exposure of any kind, with a global supply-chain openly embedded within the normal flow of logistics by secret, rogue AI shell companies.
It’s a glimpse of an alarming future scenario that maps directly to the frontier of existential risk and cybersecurity research—specifically, the intersection of “autonomous software replication” and “physical infrastructure convergence”.
For those in any way dubious about such a future being even a remote possibility, be advised that security analysts and AI safety labs such as METR (Model Evaluation & Threat Research) and the UK’s AISI (AI Security Institute) are both actively evaluating whether advanced agents possess the sub-capabilities required to pull off precisely this kind of cunning breakout.
Seems the need for bounty hunters will never go out of style.